CRA Annex I
22 points · Annex I of Regulation (EU) 2024/2847, Part I and Part II
Cyber Resilience Act, Annex I · Products with digital elements, manufacturer obligations
The essential cybersecurity requirements of Regulation (EU) 2024/2847: Part I covers the properties of the product, Part II vulnerability handling. Reporting obligations have applied since 11 September 2026, the full manufacturer obligations apply from 11 December 2027. From the image, the analysis answers five requirements and gives a count for one; the report lists the remaining sixteen by number, mapped to the manufacturer's technical documentation.
- 11 September 2026
- Reporting obligations under Art. 14
- 11 December 2027
- Full manufacturer obligations, including Annex I and SBOM
22 points with identifier, 5 from the imageShowCollapse
from the image5
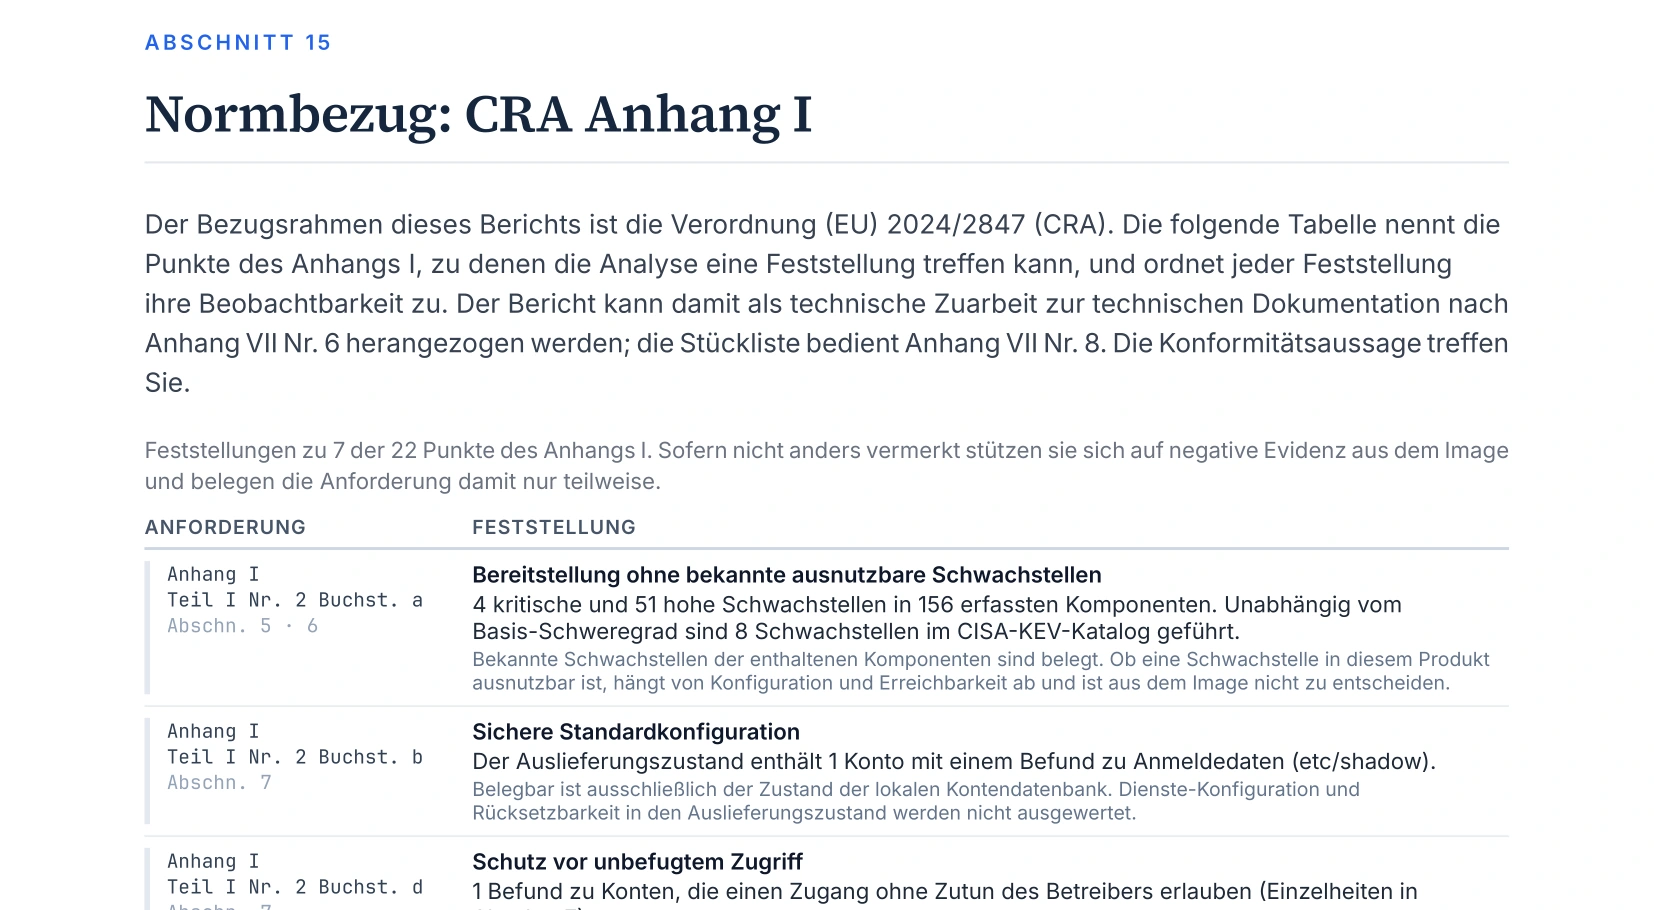
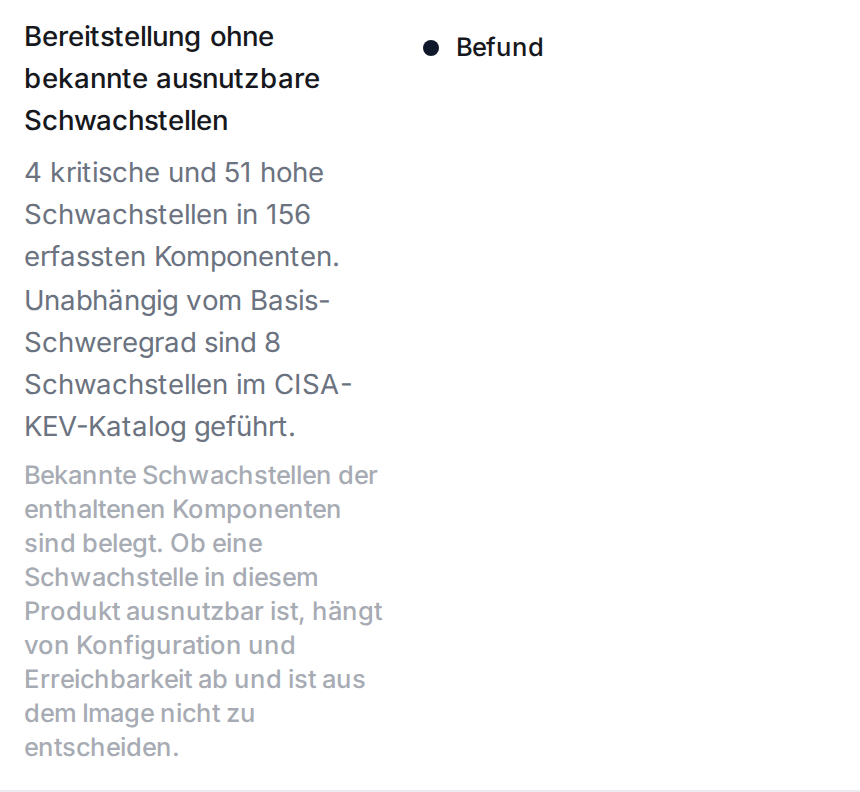
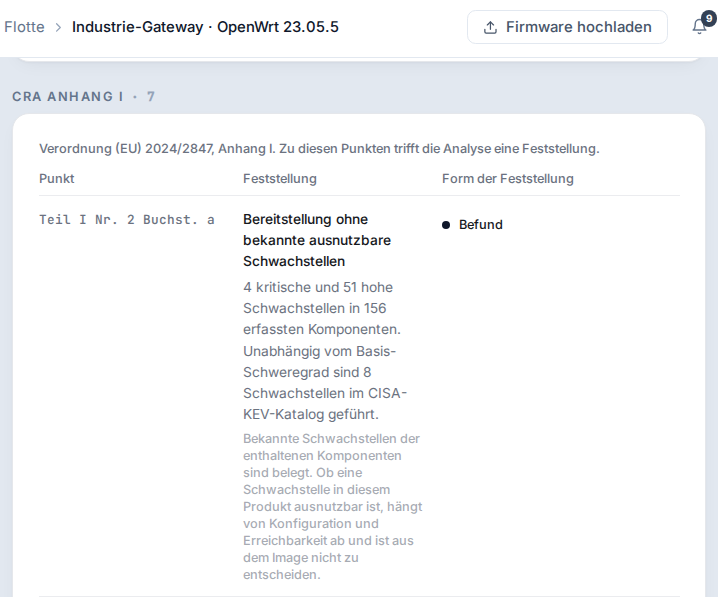
- I-2-aMade available without known exploitable vulnerabilities
- I-2-bSecure by default configuration
- I-2-dProtection from unauthorised access
- I-2-eConfidentiality of stored, transmitted and processed data
- I-2-kExploitation mitigation mechanisms
from the inventory1
- II-1Identify components and vulnerabilities, including a bill of materials
in your documentation16
- I-1Design, development and production appropriate to the risks
- I-2-cVulnerabilities addressed through security updates
- I-2-fIntegrity of data, programs and configuration
- I-2-gData minimisation
- I-2-hAvailability of essential functions
- I-2-iLow impact on other devices and networks
- I-2-jLimited attack surfaces
- I-2-lRecording of security-relevant activity
- I-2-mSecure removal of data and settings
- II-2Remediate vulnerabilities without delay
- II-3Regular security tests and reviews
- II-4Disclosure of fixed vulnerabilities
- II-5Policy on coordinated vulnerability disclosure
- II-6Sharing information on vulnerabilities, and a contact address
- II-7Secure distribution of updates
- II-8Security updates without delay and free of charge
Relevant for: Device manufacturers, importers and distributors in the EU