Managed service providers · MSSPs
Firmware analysis for your customers' devices
Since 6 December 2025, managed service providers are covered by the BSIG themselves, and customers under NIS2 must secure their supply chain under § 30 BSIG (Germany's NIS2 implementation). LegacyMind analyses the firmware of your customers' devices and prints, per device, the report you hand on.
As of 20 October 2026 · BSI Act as amended by Germany's NIS2 Implementation Act (NIS2UmsuCG)
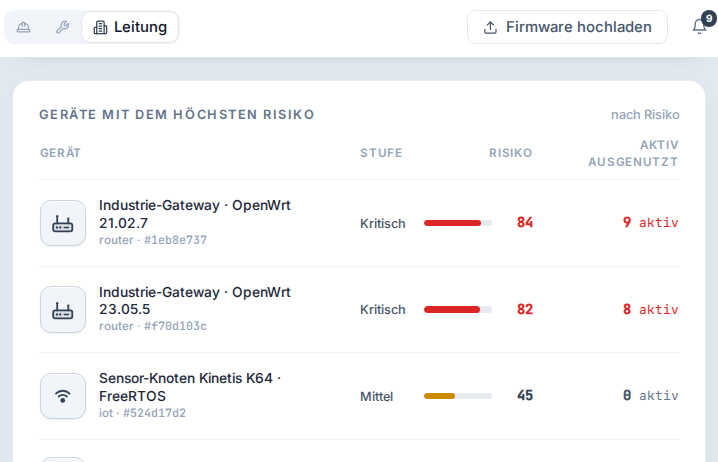
One list
All your customers' devices in one place
Every analysed device with its version and SBOM. Here, five devices we analysed between July and August 2026.
| Device | Components | Analysed |
|---|---|---|
| NASFirmware 4.5.x | 1,712 | 27 July 2026 |
| Industrial router00.07.x | 565 | 26 July 2026 |
| Industrial router00.01.14.5 | 485 | 22 August 2026 |
| ControllerFW30 v04.08.09 | 467 | 30 August 2026 |
| ControllerFW28 v04.06.01 | 434 | 30 August 2026 |
What you hand on
One report per device for your customer
The report carries the findings your customer needs: CRA Annex I as a manufacturer, § 30 BSIG as an operator.
Technical findings report
PDF per device, with components, vulnerabilities, hardening and the findings against CRA Annex I or § 30 BSIG, depending on your customer's role.Management summary
PDF per device, for your customer's management.SBOM
CycloneDX or SPDX per device, for your customer's documentation.
Many firmware files
Up to 20 firmware files in one upload
A new customer rarely brings just one device. The batch upload takes up to 20 files at once. What happens to the files is described under Security and confidentiality.
- 20files
- in one batch upload
- 2GB
- per file
What your customers need
The firmware is part of their supply chain
The devices you look after run firmware your customer did not build itself. That is exactly what § 30 asks about.
§ 30(2) no. 4
Supply chain security
Your customers must evidence the security of their supply chain. The firmware of the devices you look after is part of it.§ 30(2) no. 5
Security in acquisition, development and maintenance, including vulnerability management
Vulnerability management in acquisition and maintenance: which known vulnerabilities sit in the components of the devices, and which come first.CRA, Art. 14
Manufacturers' reporting obligations
Since 11 September 2026, customers who build devices themselves must report actively exploited vulnerabilities within 24 hours. For that they need the SBOM per release.
What applies to you
MSPs and MSSPs in the BSIG
Whoever operates or secures networks and systems for others is a managed service provider or managed security service provider under § 2 BSIG, and has obligations of its own once it reaches the size of an important entity.
- Annex 1
- Managed service providers and managed security service providers are listed in Annex 1 (nos. 6.1.10 and 6.1.11), sector digital infrastructure.
- Important
- Important entity: a type of entity from Annex 1 or 2, with 50 or more employees or with annual turnover and annual balance sheet total each above EUR 10 million (§ 28(2)).
- Particularly important
- Particularly important entity: a type of entity from Annex 1, with 250 or more employees or with annual turnover above EUR 50 million and annual balance sheet total above EUR 43 million; operators of critical facilities regardless of size (§ 28(1)).
- Measures
- For MSPs and MSSPs, an EU implementing regulation specifies the risk management measures; it takes precedence over § 30(2) (§ 30(3)).
- 24 hours
- Early first report of a significant security incident (§ 32(1) no. 1)
- 72 hours
- Notification with an initial assessment, its severity and impact (no. 2)
- 1 month
- Final report after the notification (no. 4)
- Management
- Management must implement the measures, monitor their implementation and take part in training regularly (§ 38).
Questions from service providers
What MSPs and MSSPs ask us
Do we fall under NIS2 ourselves as an MSP?
Managed service providers and managed security service providers are listed in Annex 1 of the BSIG. From 50 employees or with turnover and balance sheet total each above EUR 10 million, you count as an important entity; with 250 or more employees, as a particularly important one.
How many firmware files can we upload at once?
Up to 20 in one batch, each up to 2 GB.
Can colleagues work in the app too?
Yes. We set up your organisation, and its admins invite members, with the role admin or member. Members see the organisation's devices and results as well.
Which reports do we hand on to our customers?
Per device a technical findings report and a management summary as PDF, plus the SBOM as CycloneDX or SPDX. The report carries CRA Annex I for manufacturers and § 30 BSIG for operators.
How do we get the firmware of our customers' devices?
From the device manufacturer's download area, where there is one. For devices on the network, the Firmware Extractor reads the firmware over SSH; it is in closed beta.
What happens when a new vulnerability becomes known?
New vulnerabilities are matched to the firmware versions already analysed: the catalogues of actively exploited vulnerabilities every two hours, new CVEs daily.
Start with one of your customers' devices
The CRA readiness check is free. You get the report and SBOM within three working days of the upload.