About us

Firmware analysis from Ingolstadt

LegacyMind reads the firmware that connected devices ship with and tells you what is inside. For device manufacturers, operators and IT service providers.

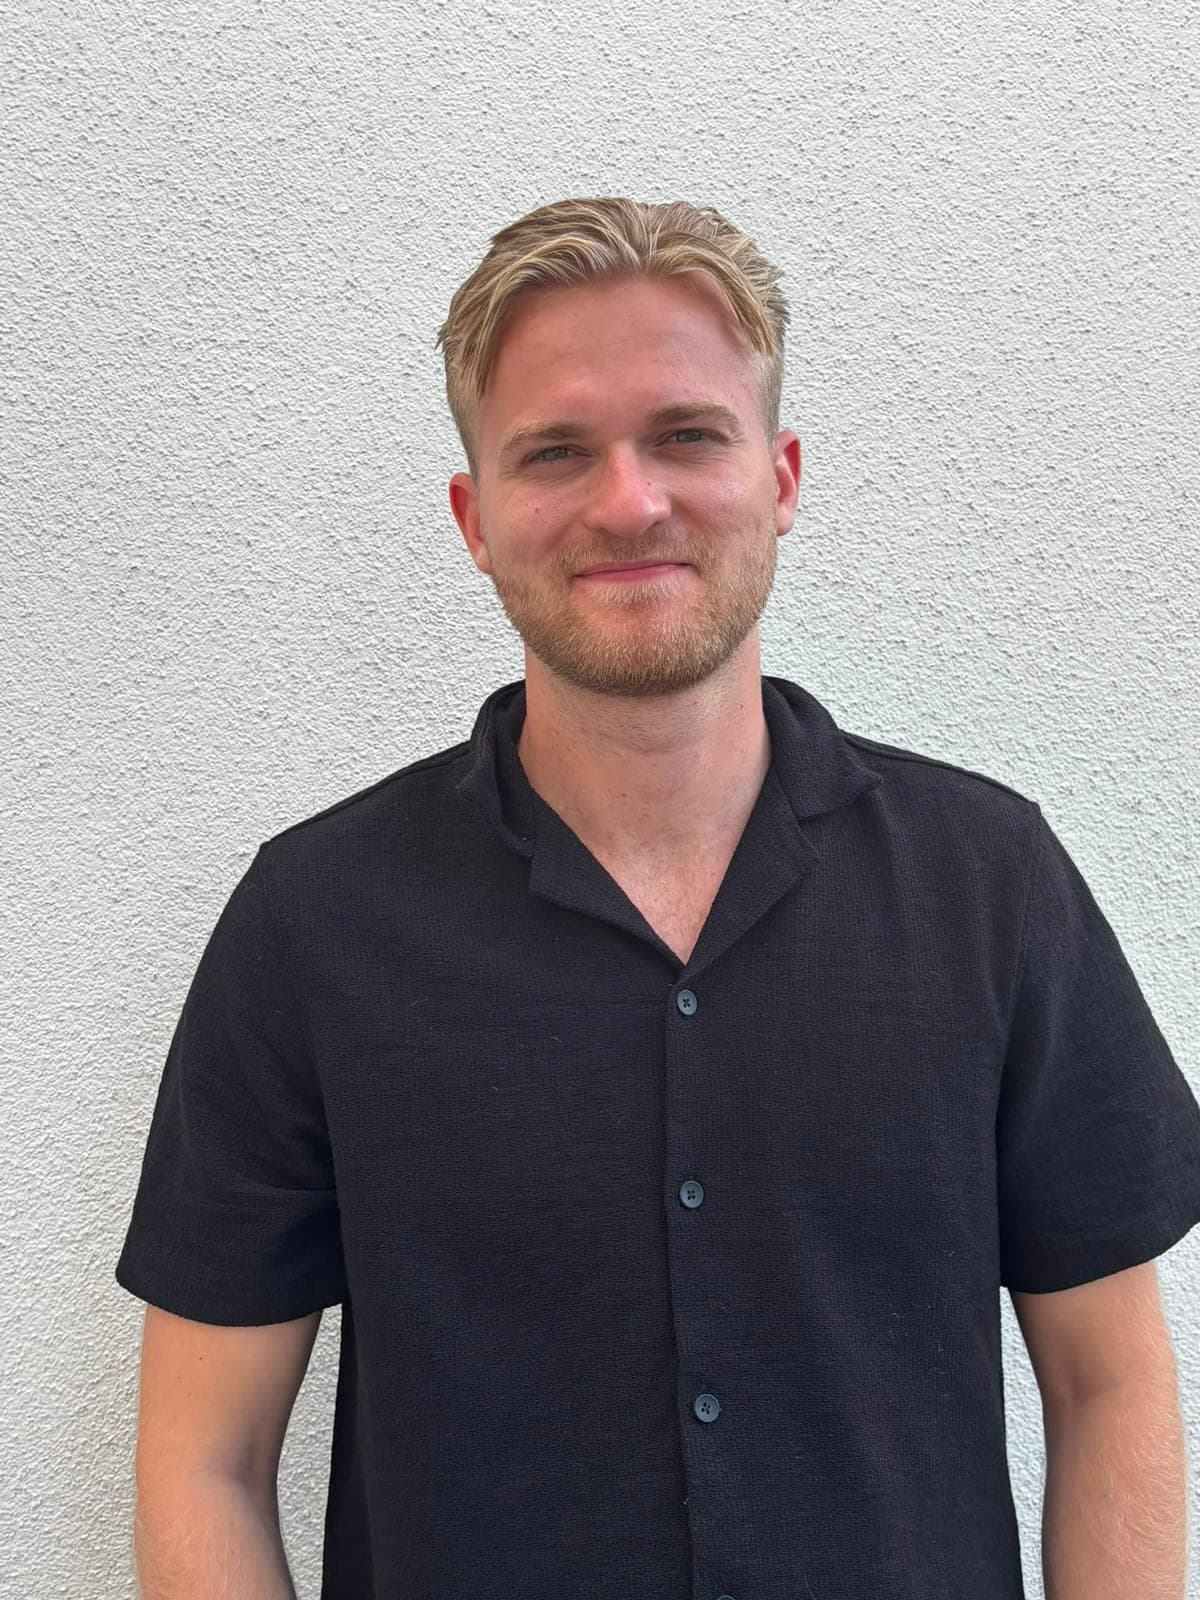
  • Ben Plannet, CTO of LegacyMind

    Ben Plannet

    CTO

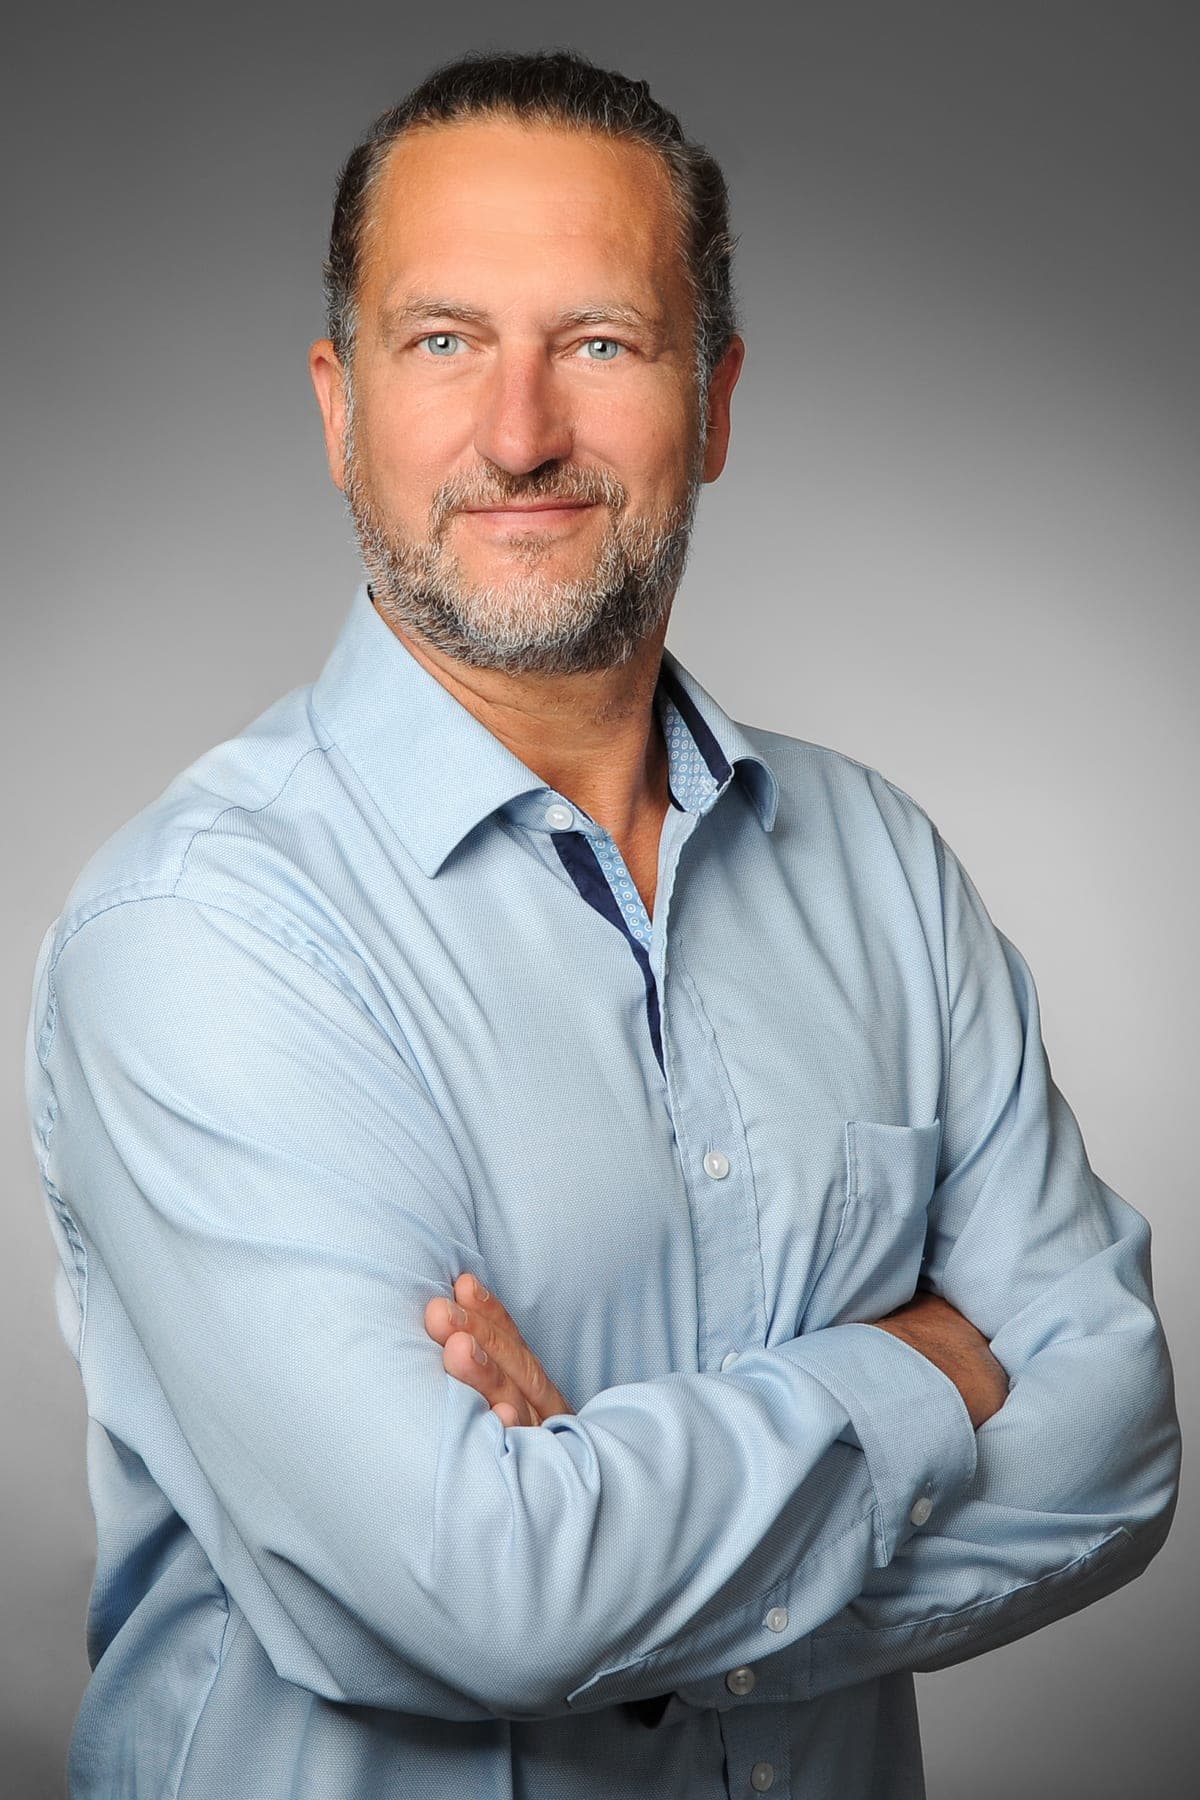
  • Marco Plannet, Managing Director of LegacyMind

    Marco Plannet

    Managing Director

01/Mission

Knowing what is inside the device

Connected devices run for ten to twenty years. Much of their firmware is made of components from suppliers and open source, and a new vulnerability can become known in any of them at any time. The Cyber Resilience Act and NIS2 turn this into an obligation: manufacturers and operators must know and document what is in their devices.

LegacyMind analyses the firmware as shipped, without source code, and keeps the result current over the whole lifecycle: software bill of materials, known vulnerabilities, hardening findings and a report you can pass on to customers, auditors and authorities.

02/Management

Management

CTO

Ben Plannet

A developer for more than ten years, coming from penetration testing, now focused on the software inside connected devices.

Responsible for the product and the analysis technology: Linux firmware, microcontroller builds from Keil, IAR and GCC, and supplier SBOMs. The person to talk to for technical conversations and live analyses.

Ben on LinkedIn

Managing Director

Marco Plannet

Almost 30 years in international IT environments, originally infrastructure, security and information security.

Responsible for running the company and for partnerships.

Marco on LinkedIn

03/Principles

What we hold ourselves to

  1. 01

    Vulnerabilities from public sources

    We match against 18 public sources: Linux distributions, vendors, government agencies and vulnerability databases. We mark a vulnerability as actively exploited only when a public catalogue of exploited vulnerabilities lists it.

  2. 02

    Your firmware stays in Germany

    The file sits in our storage in Frankfurt and is analysed on our servers in Germany. Only the component name and version go out. We delete the file after the analysis.

  3. 03

    The report shows what was checked

    The report states which parts of the image were analysed. If a part cannot be read, it says which part and why.

  4. 04

    Findings, no percentage

    For every point of CRA Annex I and § 30 BSIG (Germany's NIS2 implementation), the report states what the analysis found, or why the point cannot be checked on the image. There is no percentage.

  5. 05

    Encrypted images stay closed

    We do not decrypt an image its manufacturer has encrypted.

  6. 06

    We measure ourselves against public data

    We check our results continuously against public references. Where they differ, we fix the product.

04/Company

The company

Company
LegacyMind GmbH
Registered office
Falkenstr. 10, 85049 Ingolstadt
+49 176 81152657
Commercial register
HRB 12510
Amtsgericht Ingolstadt
VAT ID
DE458254926

The register number and VAT ID are also in the Impressum (German).

05/Contact

Check your own firmware

We analyse one firmware file from your portfolio and go through the result with your team.